 Varlatch
Assisted mode
varlatch --assistedYou approve
Keyling runs the CLI
Your app gets the values
What Keyling sees
charging with [REDACTED:STRIPE_KEY]Today, your secrets sit in .env files your coding agent can read. With Varlatch, your .env moves in, your agent sees masked output and placeholders, the secret parts come back to you, and one change syncs to every platform you connect.
Masked by default, placeholders when it needs a key. Signing in, entering a provider’s key, and showing a secret come back to you, and a change waits for your yes.
charging with [REDACTED:STRIPE_KEY]sk_live_••••gets the real keyvlch_ph_…only the placeholderSTRIPE_KEY=vlch_ph_v1_9f2c41e8…DATABASE_URL=postgres://app:Xk9qT2…
STRIPE_KEY=sk_live_51Nq8vEaR…
SESSION_SECRET=9f2c41e8a7b3d0…
your laptop
STRIPE_KEY=sk_live_51Nq…
a teammate’s laptop
STRIPE_KEY=sk_live_51Nq…
#dev chat
STRIPE_KEY=sk_live_51Nq…
CI cache
STRIPE_KEY=sk_live_51Nq…
last year’s backup
STRIPE_KEY=sk_live_51Nq…
your coding agent
STRIPE_KEY=sk_live_51Nq…
Every machine keeps .env files: copied from chat, backed up, sometimes committed.
varlatch import moves them in without printing a value; varlatch run hands values to your app’s process only.
You paste a key into the agent chat. Now it is in the context, the logs, and the history.
Your agent hands you a command for your own terminal, which asks for the key without showing it.
An agent with a shell can cat .env and read your production key.
Launched agent-safe, it holds placeholders. The Broker adds the real key only for hosts you allow.
Rotating a key means five dashboards, and an outage when you miss one.
Rotate once with a grace period; Varlatch pushes the new key to Coolify, GitHub Actions, and Convex.
A new teammate gets the .env in a chat message, and keeps it after they leave.
Invite them instead: a passkey, and a grant for exactly the environments they need.
A missing or malformed value passes review and crashes production on boot.
A typed Contract: generated types in your code, and varlatch validate fails CI first.
Compromise the database or the dashboard and every secret goes with it.
Only varlatchd decrypts, and its root key is not in the database.
When a key leaks, nobody can say who had it.
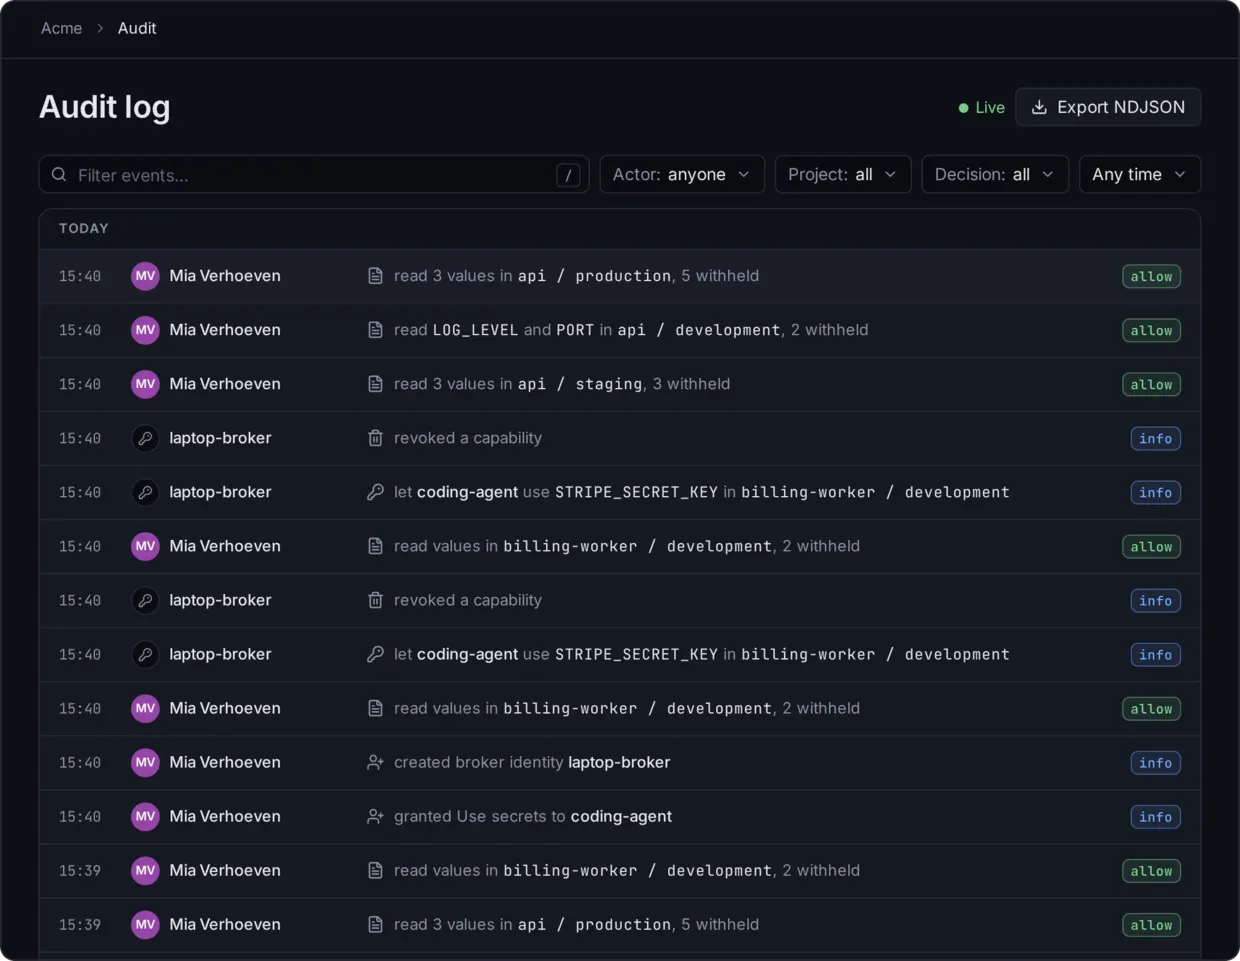
Every use, reveal, and denial is recorded in an append-only audit log.
Self-hosting means TLS, keys, untested backups, and scary upgrades.
varlatch setup takes a fresh host to a running installation; backups are encrypted and verified.
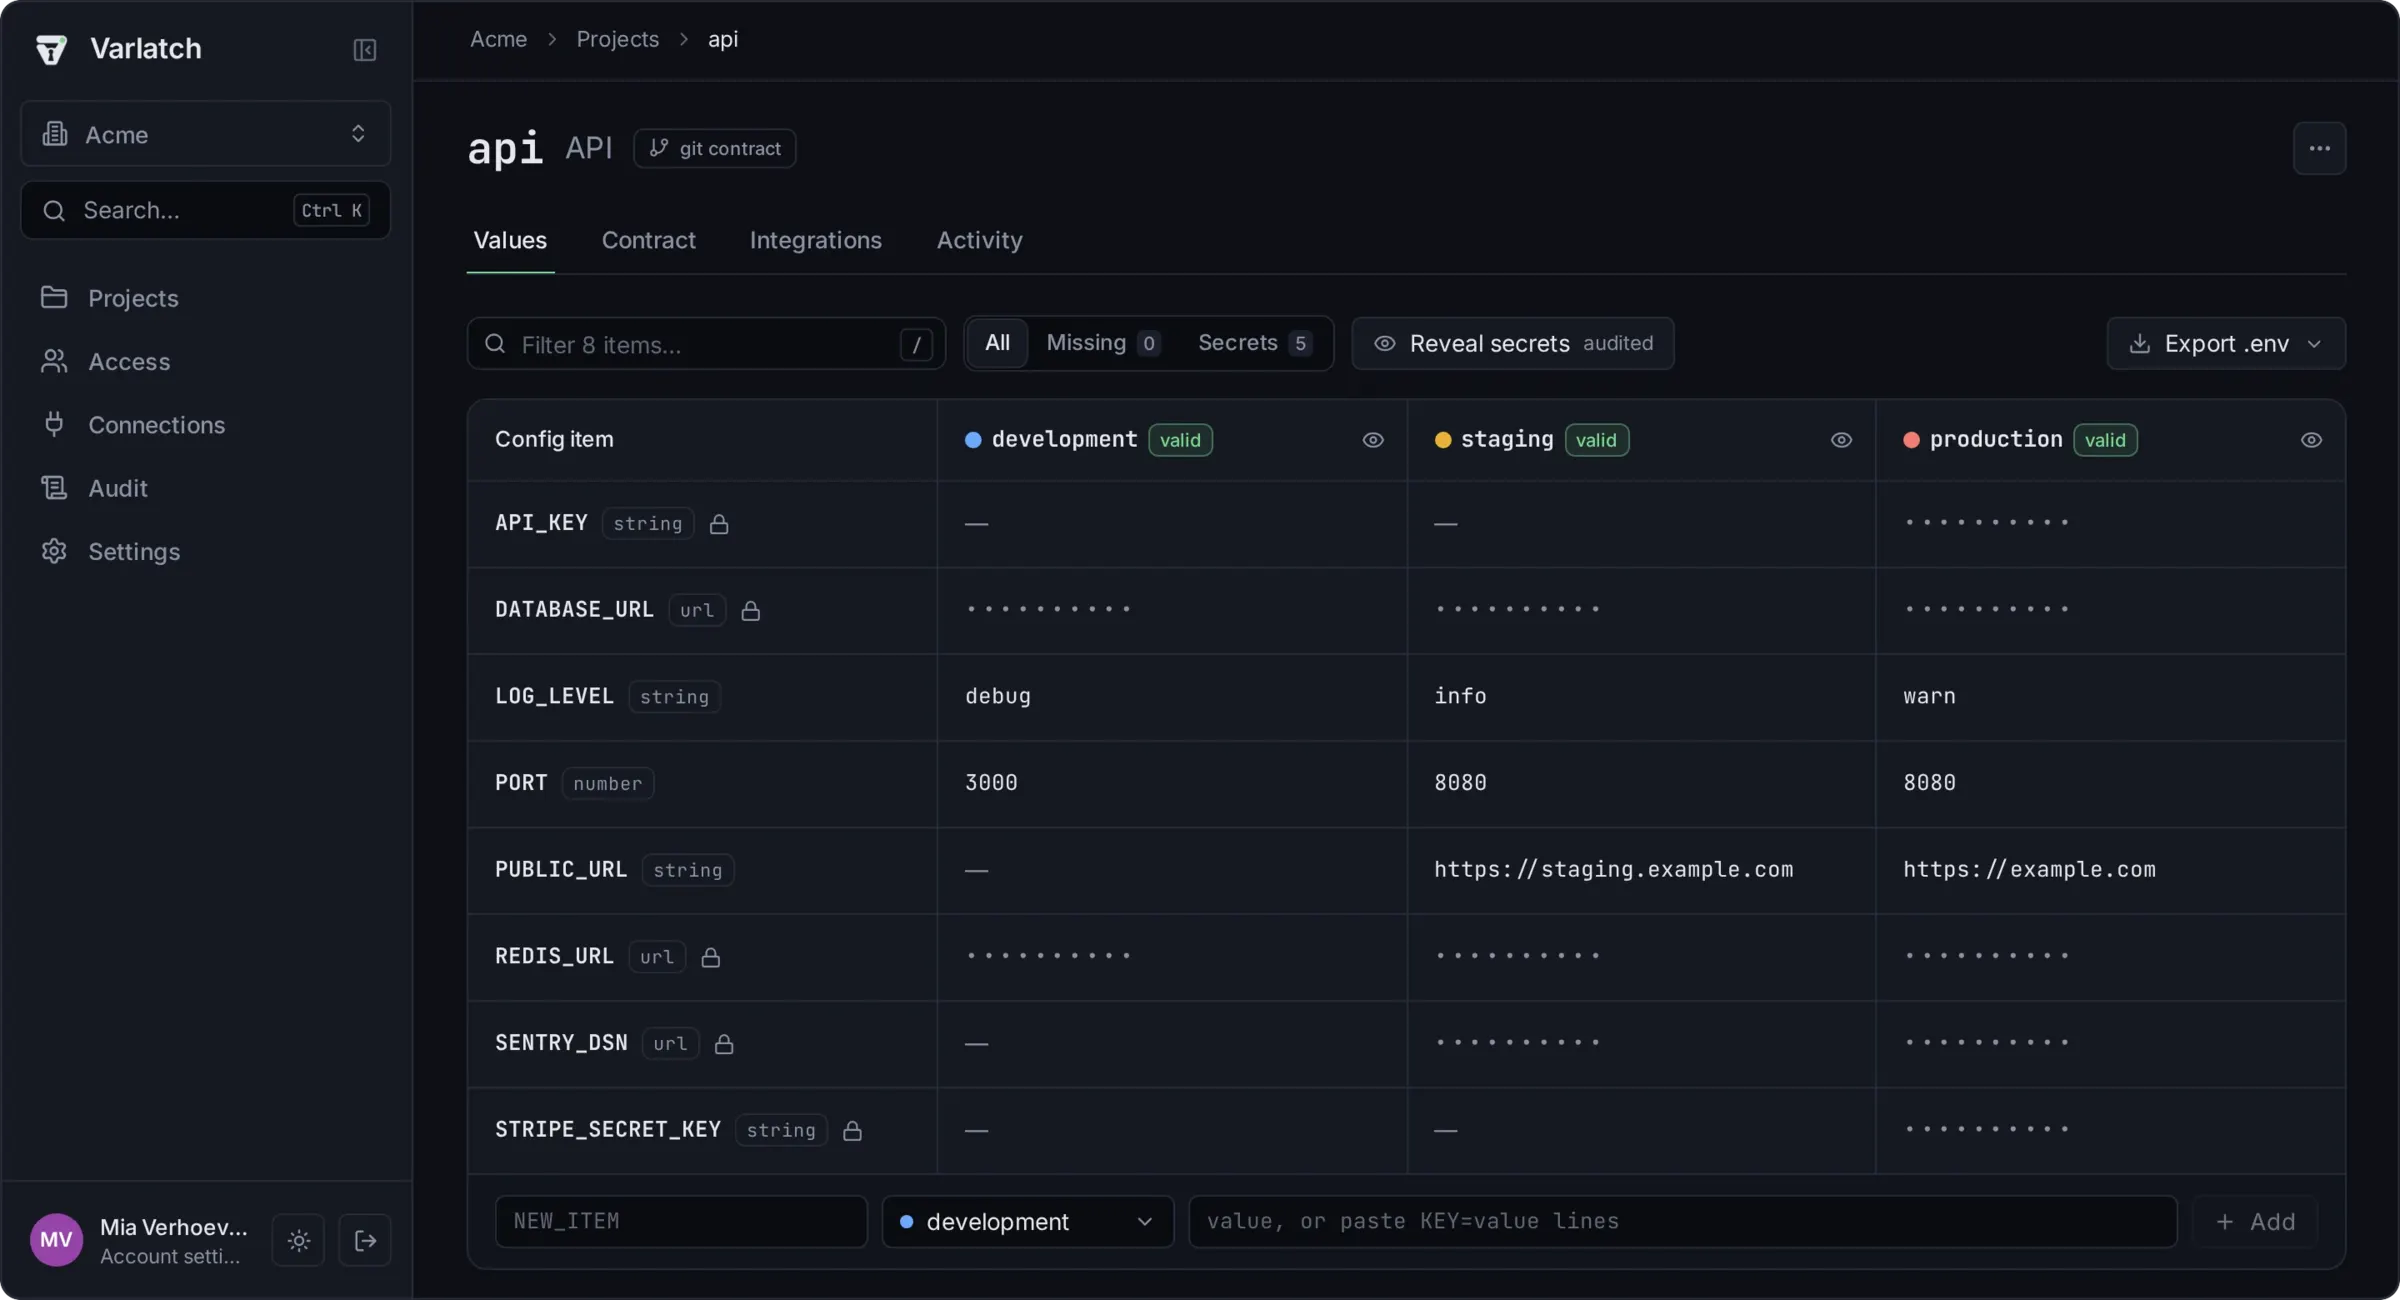
api / production
STRIPE_KEYstring
••••••••••rotated · grace 1h
.env.schema (how).Varlatch is free to self-host. One person runs the installation, and everyone else connects to it with the CLI and a passkey.
1Your server
$ varlatch setup
every key it needs, generated
the first passkey, yours
2Your repository
$ varlatch init
connected to a project
the Varlatch skill for your agent
3Your app
$ varlatch run -- npm run dev
its values, in its environment
no file of secrets written
Give it this, with your server’s address. It installs the CLI, connects the repository, and moves your .env files in. You approve the sign-in with your passkey and type any secret it does not have.
Setting up the server itself stays with you. Setup by a coding agent has not been evaluated yet; the evaluation covers agents using the CLI.
Set up Varlatch in this repository, following
https://docs.varlatch.com/set-up-with-an-agent/
Our Varlatch server is https://vault.example.com
A Linux server with Docker, and the CLI for Linux, macOS, or Windows (requirements). Already invited? Join a project.
Read the getting-started guideDownloads
Host one installation for your team. Connect from the CLI, with an optional desktop companion to keep your sessions close.
Your server can run on a different machine.
All platforms ↓Linux server · amd64 / arm64
The server and dashboard, packaged for Docker Compose. You keep the keys.
Requires a Linux host with Docker Compose 2.24 or newer.
macOS · Linux · Windows
Connect projects, run apps with their configuration, and work with your coding agent.
Use the release your server runs and a supported, patched Node.js version. Node 22 requires at least 22.23.4.
macOS
See your sessions and expiry times, sign in, renew, and sign out from the menu bar.
brew install varlatch/tap/varlatch varlatch/tap/varlatch-menubarWindows · x64 / ARM64
Keep your Varlatch sessions in the notification area, with quick sign-in and renewal.
Choose your architecture on the release page. The installation guide covers the CLI and prerequisites.
Linux · Omarchy
Your sessions in the Omarchy bar, with expiry notifications and quick sign-in, renewal, and sign-out.
omarchy plugin add https://github.com/varlatch/omarchy-plugin.git --enableThe desktop apps connect to an existing Varlatch server. Before installing release files, follow the signature and checksum verification guide. Each companion app also documents its installation and verification steps.
Not on the documented flow. In assisted mode the CLI never prints a secret value, refuses one on the command line, and masks secrets in the output of the commands it runs. Launched agent-safe, the agent holds placeholders only. Assisted mode protects against accidents: your agent runs as you, so your approvals are what stop deliberate misuse.
It stops and hands you a command for your own terminal, such as varlatch values set STRIPE_KEY -e production, which asks for the value without showing it. A value Varlatch can create, like a session key, the agent can generate with --generate after you approve; nobody sees it.
varlatch init gives your agent the Varlatch skill, in the open Agent Skills format, and a block in AGENTS.md: plain text with shell commands and no agent-specific tools. Optional guardrails add hooks for Claude Code and Codex, as a second line against accidents. The CLI recognises Claude Code, Codex, Cursor, Copilot, Gemini CLI, and OpenCode sessions and turns assisted mode on by itself. In a dated baseline evaluation (October 2026, Varlatch 0.14.3), the command-line coding agents Claude Code 2.1.278 with Claude Sonnet 5.5 and Codex CLI 0.160.1 passed all 40 cases, 20 each, with no hooks, against a local test server (what was evaluated). Other coding agents, other versions, and editor or cloud interfaces have not been evaluated.
Yes. Everything your agent does is a plain varlatch command or a click in the dashboard. The agent only saves you the typing.
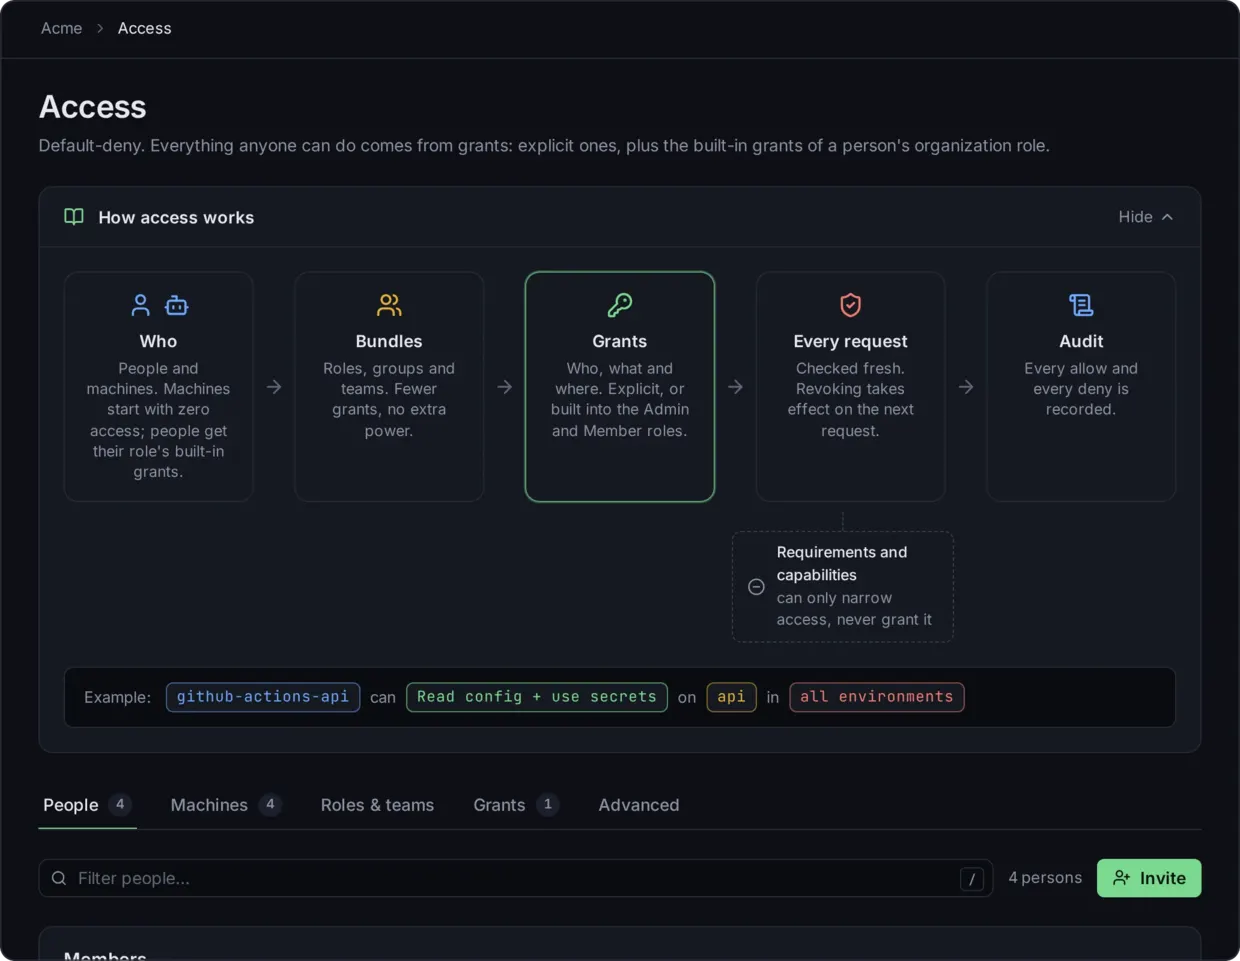
Nobody, until you grant it. Access is default-deny for people and machines alike: you grant each one exactly the environments and actions it needs, directly or through custom roles, groups, and teams. Using a secret and revealing it are separate permissions, so a machine can run with a key it is not allowed to show. A Tailnet Requirement can also limit an environment to machines you choose on your Tailscale network, checked by Tailscale identity rather than by IP address.
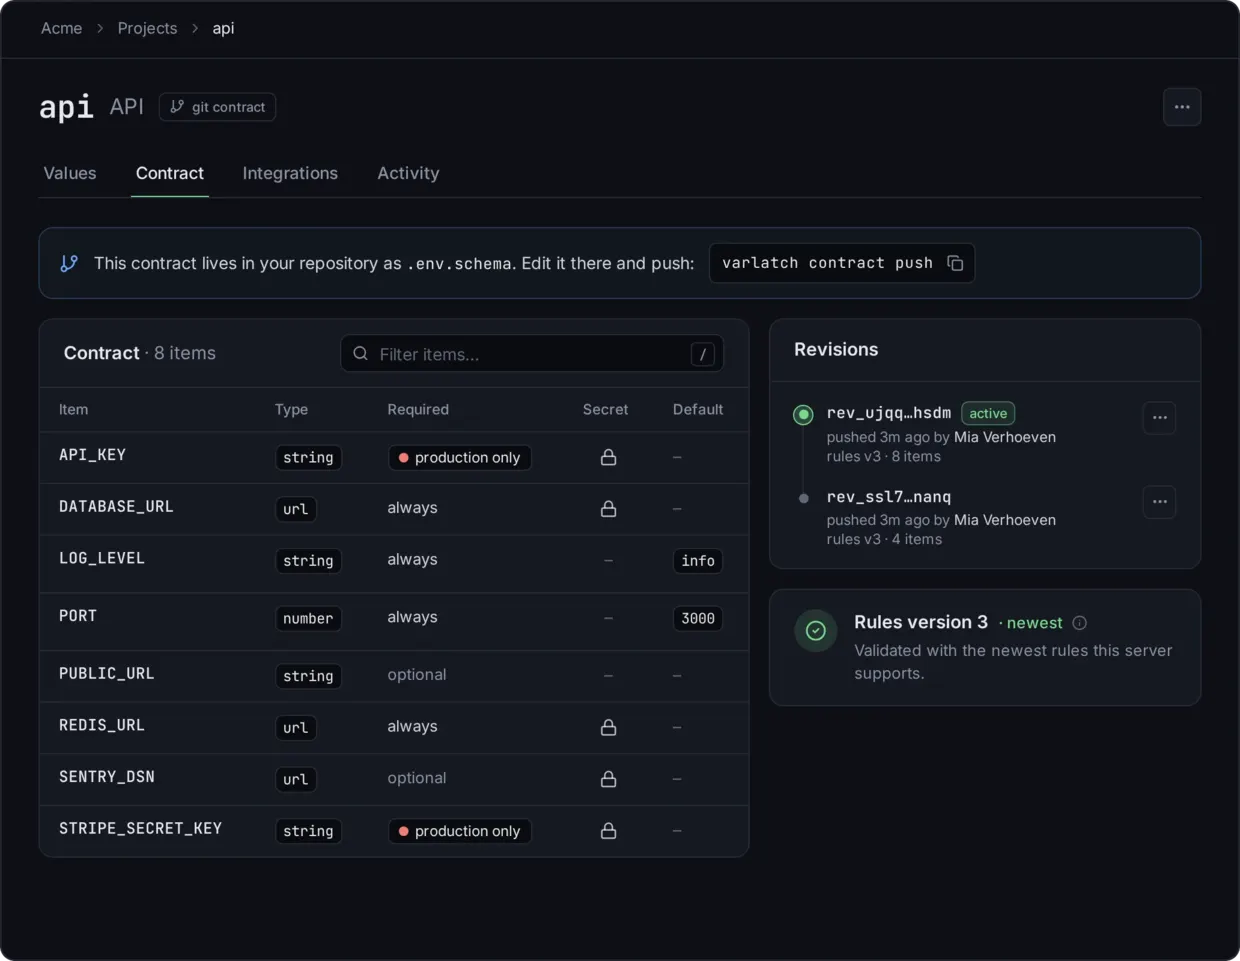
Yes, as the project's Contract: a .env.schema file in your repository that says which items your app needs, of what type, whether each is required and in which environments, and which are secret. Items are secrets unless marked @public. Change it in a pull request, then push it with varlatch contract push and activate the new revision. varlatch types generates TypeScript or Python from the Contract, and varlatch validate fails CI when an environment is missing a required value or holds an invalid one. You can also edit the Contract in the dashboard instead. The .env.schema format comes from @env-spec, which DMNO created for Varlock; Varlatch reads a subset of it with its own parser.
Only for an MCP host that gives its model no shell. A coding agent with a shell uses the CLI directly, in assisted mode. varlatch mcp ships inside the CLI for the others.
Varlatch's own code is. The server and dashboard are AGPL-3.0, and the CLI and SDKs are Apache-2.0 (license). By default Varlatch runs on the Convex backend, which is source-available, not open source: its license, FSL-1.1-Apache-2.0, permits internal use, which includes running Varlatch for your own organization, and each version becomes Apache-2.0 two years after its release.
You can check. The code is public, and so is the threat model: what Varlatch guarantees, what it assumes, and what it does not protect against. Releases after 0.15.0 are signed by the release workflow, keyless through Sigstore, and each image carries build provenance and an SBOM: verify a release with cosign before you install it. Report a vulnerability privately, through GitHub or security@varlatch.com, as the security policy describes.